


Tariq Saeedi
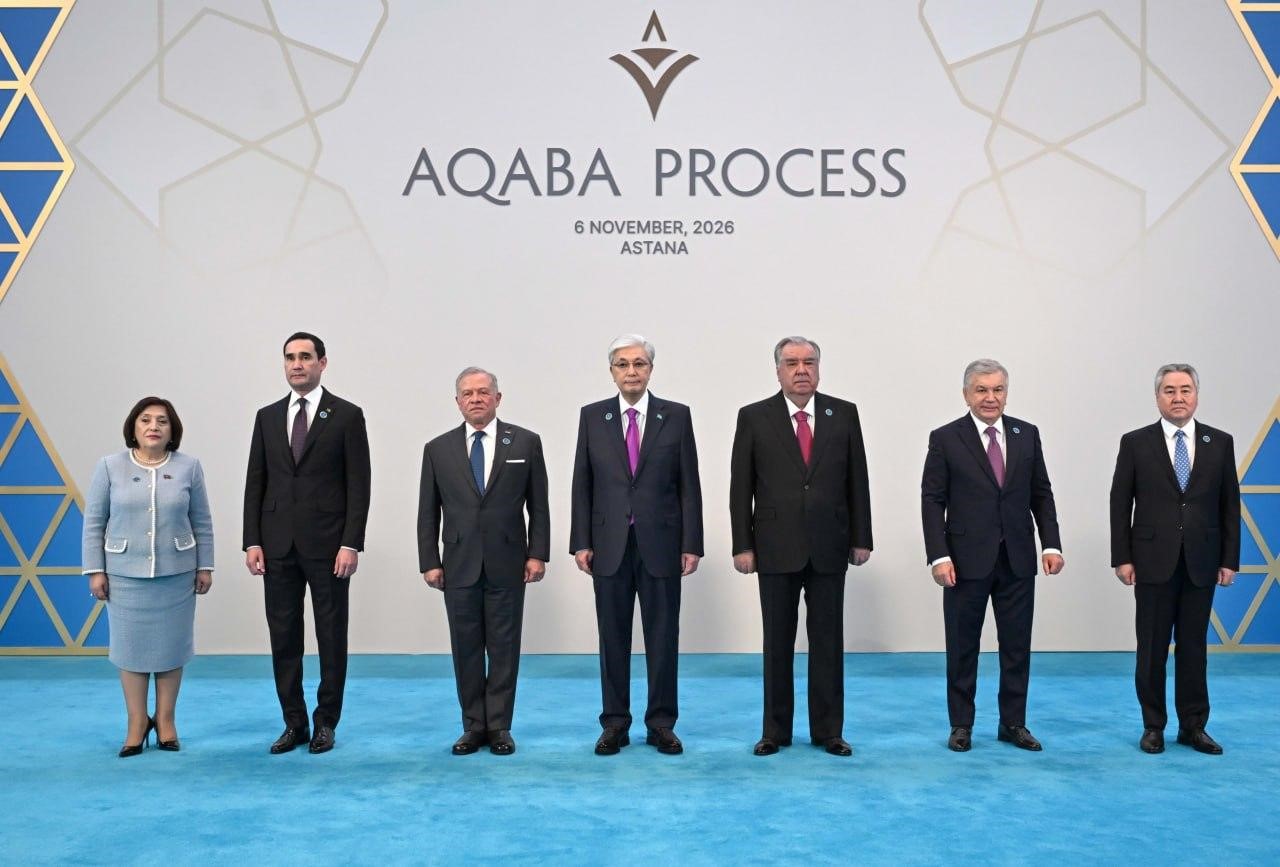
The Aqaba Process meeting in Astana on November 6, 2026, brought leaders from Central Asia, Jordan, and Azerbaijan together to tackle a reality we can no longer separate from national and international security: artificial intelligence.
While AI is transforming economic development, healthcare, and public administration, it is fundamentally altering how information is produced, interpreted, and weaponized—extending deep into cyber defense, counterterrorism, and critical infrastructure.
Security Threats are Evolving in Scale and Form
AI doesn’t invent crimes like fraud, propaganda, or espionage; rather, it supercharges their speed, scale, and accessibility.
Malicious actors can now automate tasks, multi-lingual disinformation campaigns, and victim profiling far more efficiently.
However, AI tools remain uneven, prone to error, and reliant on human intent.
As France’s ANSSI and the UK National Cyber Security Centre warn, while AI aids attackers in social engineering and cyber operations, it also introduces systemic vulnerabilities of its own.
Crucially, the arrival of AI doesn’t replace old weaknesses—basic cybersecurity hygiene remains our strongest frontline defense.
Information Manipulation and the Erosion of Trust
Beyond technical hacks, generative AI lowers the cost of fabricating text, audio, and video to mimic real leaders or institutions. Even crude synthetic content can spark panic if timed to coincide with public anxiety.
While organizations like the OECD flag manipulation as a core risk, not every synthetic campaign alters political outcomes; speculation must be separated from evidence. The true crisis centers on trust: as AI compresses the evaluation process into a single synthesized answer, it obscures whether an output is verified fact, interpretation, or outright error.
Expanding the Strategic Space of Security
Security is no longer just about guarding physical borders or server networks—the information environment is now a strategic space. A single fabricated report or false emergency broadcast can destabilize public order. Yet, protecting society cannot mean censoring legitimate disagreement or treating every challenge to official narratives as hostile.
The objective must be to protect the conditions for informed judgment, ensuring transparency, source visibility, and the right to question authority.
Future Trajectories: Agents, Personalization, and Interconnection
As AI capabilities mature, risks will shift:
- Cyber & Agent Operations: Autonomous AI agents granted direct access to emails, databases, or industrial software could turn minor coding errors into high-impact operational disruptions if deployed without strict human oversight.
- Synthetic Identities & Personalization: Tailored influence campaigns will exploit user data to target communities with micro-targeted narratives, threatening both individual privacy and collective stability.
- Interconnected Failures: As critical infrastructure increasingly relies on shared AI models, a single software bug or corrupted data input can cascade across multiple vital services.
- Emerging vs. Proven Risks: While international assessments (like the International AI Safety Report 2026) flag long-term biological or chemical risks, policy must remain anchored in demonstrated capabilities rather than ungrounded speculation.
A Practical 6-Stage Framework for Risk Management
To prevent harm without choking technological innovation, institutions should adopt a continuous risk-management methodology:
- Identify: Audit what systems process, who operates them, and what actions they can take.
- Assess: Evaluate realistic threat likelihoods and potential consequences.
- Protect: Implement life-cycle cyber controls, access limits, and mandatory human-in-the-loop approvals for high-impact decisions (utilizing frameworks like ISO/IEC 27090:2026 and the NIST AI RMF).
- Verify: Check output reliability, trace information origins, and treat flagged uncertainties transparently.
- Respond: Maintain clear protocols for incident reporting, system suspension, and error correction.
- Review: Continuously reassess systems as operational environments evolve.
Information Literacy, Institutional Credibility, and Cooperation
Technical safeguards alone are insufficient; society requires layered resilience:
- The Individual & Education: Building habits of information literacy—checking original sources, questioning emotional triggers, and verifying dates—is an essential defense.
- The Media: Newsrooms must prioritize deep verification over speed, transparently noting when AI or synthetic material is involved.
- Governments: Public institutions must lead by example, providing authenticated communication channels and rapid corrections to maintain public trust.
- Regional & International Cooperation: Because cyber threats and synthetic campaigns cross borders effortlessly, frameworks must align. Regional cooperation via platforms like the Aqaba Process is vital for sharing threat intelligence, building technical capacity, and harmonizing safety standards without infringing on fundamental rights.
The ultimate lesson of the Astana meeting is that modern security is fundamentally about safeguarding human judgment. By combining secure systems, transparent institutions, international cooperation, and an alert, critical public, society can harness AI’s immense development potential while preserving the freedom and truth that security is meant to protect.
The real objective is not to create a world in which people are told what to believe. It is to create a world in which they have the means to determine what deserves to be believed. /// nCa, 7 November 2026 (photo credit – Akorda)